
在局域网中部署的专用传感器节点「RoamSwitch Sensor」
RoamSwitch Sensor 是部署在局域网内的专用节点,从外部审计同一局域网上的 RoamSwitch 终端(Mac / Linux Client / Server Edition)。会确认「从同一局域网的其他设备看过来是什么样子」(开放端口、无需认证即可访问的服务、横向移动的立足点),这是主机自我诊断在原理上无法看到的。同时还提供局域网设备台账与 ARP 欺骗检测。
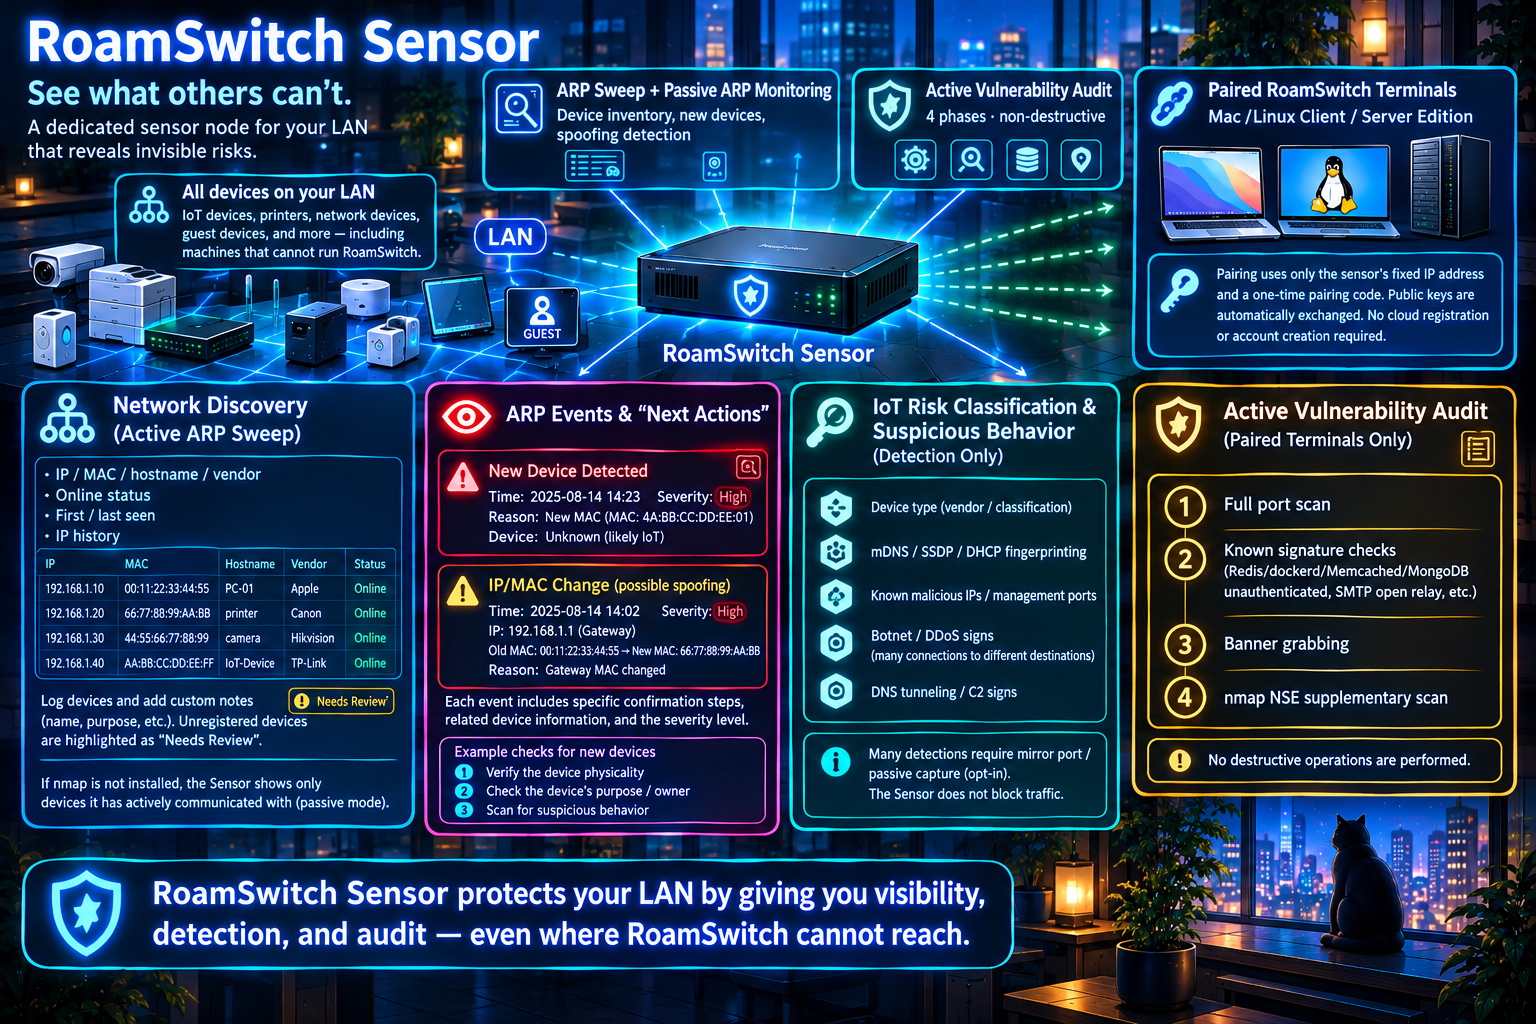
🛡️ 主动漏洞审计(仅针对已配对端点)
由全端口扫描 → 已知特征检测(Redis/dockerd/Memcached/MongoDB/Elasticsearch/CouchDB/Jenkins/VNC 未授权暴露、SMBv1 与未强制 SMB 签名、RDP 未强制 NLA、SMTP 开放中继等)→ 通用 Banner 获取 → nmap NSE 补充扫描共 4 个阶段构成,全程不含任何破坏性操作。
📋 掌握网络构成(主动 ARP 扫描)
通过 ARP 扫描找出局域网内的设备。将 IP、MAC、主机名、厂商、在线状态、首次/最近发现时间和 IP 历史整理成设备清单,并可为每台设备自由填写名称、用途等备注。没有备注的设备会被标为“需确认”,可用于与资产清单核对。未安装 nmap 时,会退回到只显示 Sensor 自己通信过的设备的被动模式。
👁️ ARP 事件与“下一步操作”
新设备出现,以及已知 IP 对应的 MAC 变化(ARP 欺骗的迹象),会连同发生时间、严重程度(严重~信息)、判断依据、相关设备的身份和具体的核实步骤一并给出。网关 IP 的 MAC 变化被视为“严重”。启用可选的被动抓包后,还能检测单台设备对大量 IP 发送 ARP 请求(内网侦察)。
🔎 掌握局域网内其他设备与可疑行为(仅检测)
以参考信息的形式给出:MAC 厂商与设备类别、依据 mDNS/SSDP/DHCP 自我通告的型号识别、连接已知恶意 IP 或管理端口、僵尸网络/DDoS 参与迹象(连接大量目的地)、DNS 隧道/C2 迹象。多数功能需要启用可选的被动抓包配置(如镜像端口),且 Sensor 不会阻断任何流量。
🔑 配对码方式(Ed25519、固定 IP、证书固定)
初始状态下不信任任何对象。端点侧输入由 Sensor 操作员发放、有效期 10 分钟的一次性配对码,并同时输入 Sensor 的固定 IP 地址以及 Sensor 屏幕上显示的证书指纹,即可一次操作建立双向信任。公钥会自动交换,无需事先获知。无需云端注册,也无需创建账户。
🔐 控制 API 防护(TLS 1.3、证书固定、防重放)
与端点之间的控制通信(TCP 50543)通过 TLS 1.3 接受(control.tls: off / optional(默认)/ required)。证书为自签名,信任由端点侧固定(pin)Sensor 屏幕上显示的指纹来决定,不会通过网络自动获取。审计请求的签名采用带时间戳和 nonce 的 v2 格式,可拒绝重放;配对码暴力破解以及签名失败会按来源 IP 进行锁定。是否接受旧格式(v1)签名以及监听 IP 也可以配置。
🖥️ 可操作全部功能的 10 语言 TUI
交互式 TUI 可用 10 种语言操作 CLI 的所有子命令、守护进程 IPC、所有配置键(配置编辑器、TLS 状态与证书重新生成、手动配对、通知测试)、收集器运维,以及所有事件界面(包括被动监控、IoT 行为、可疑通信、漏洞信息)。CLI 支持日语和英语。审计报告和导出也可以用 10 种语言输出。
📅 定期审计与差异对比(可选启用)
按计划自动审计所有已配对的端点,并显示与上一次审计相比的变化——新增发现、已解决项和新开放的端口。若之前开放的端口全部看不到了,将按“疑似不可达”处理,而不是“已解决”。即使无人值守,Sensor 也会在每次审计前后确认端点仍是其认证时的 MAC 地址;若该 IP 已属于其他设备,则不进行审计。默认关闭,可设置执行间隔和允许执行的时间段。
📣 通知与审计证据(可选启用)
回归、新设备、ARP 欺骗等事件可通过 Webhook(Slack、Discord、Teams 等)和 syslog(RFC 5424)发出通知。配对、解除配对、审计、配置变更会连同执行者一起记录到带防篡改检测的操作日志(哈希链)中,审计结果、设备台账和操作日志可导出为 CSV、JSON、HTML 报告(可在浏览器中另存为 PDF)。通知的发送目的地全部由运维人员自行设置,默认不会发送设备信息,也不会发送审计结果。检测用数据(CVE 映射和 nmap NSE 数据库)每天从更新服务获取,但可通过 updates.fetch_cve_map 停止,且此通信不包含设备和审计数据。
🗂️ 汇总多个 Sensor(中央收集器,可选启用)
面向在多个站点部署 Sensor 的组织,内置了汇总签名摘要的中央收集器(默认禁用)。提供按站点查看状况的仪表板和 CSV 导出,并可检测 Sensor 端审计日志的截断与回滚。未安装 RoamSwitch 的设备(非受管设备)可分类为「未配对的 RoamSwitch 主机」或「未知设备」并纳入摘要(collector.send_unmanaged_devices。不包含通信内容)。仅接受已登记 Sensor 的签名请求,且不能在没有 TLS 的情况下向局域网外公开。
🚨 非法 DHCP 服务器与 IPv6 路由器检测(仅检测)
每小时用随机 MAC 发送一个 DHCP(IPv6 为 DHCPv6)探测包,统计所有应答的服务器(不会租用 IP 地址)。会通知后来新增的服务器、分发与合法服务器不同的网关或 DNS 的服务器、由 IPv4 网关以外的设备发出的 IPv6 路由器通告、IPv6 地址持有者的变更(NDP 欺骗),以及仅在 IPv6 下可见的设备。设备台账也支持 IPv6 地址。Sensor 不会阻断任何流量。
🔎 未部署 RoamSwitch 设备的轻量审计(可选启用,仅连接检查)
对于未配对的打印机、摄像头、NAS 等设备,仅在运维人员授权的范围内,对固定的端口做连接检查并读取服务主动发出的信息。不会尝试登录或利用漏洞;OpenVAS 之类的深度扫描只对已同意(已配对)的终端进行。启用前必须先设置批准人记录和目标范围,且每次执行都会把授权记录写入审计日志。
🔒 丢失、被盗或报废时的吊销与锁定
在收集器中吊销后,该 Sensor 会在下次上传时自行停止,停止配对、审计、上传和通知(重启后依然保持停止)。还可以设置为清除密钥和存储的数据、在长期无法连接收集器时自动停止,也提供用于报废的命令。同时会显示曾与其配对的终端列表和解除配对的方法。
如需对 Sensor 自身进行攻击防护,建议在同一台机器上另行安装 RoamSwitch for Linux 的 Server Edition,两者可作为完全独立的进程共存。
审计报告输出示例
这是通过 roamswitch-sensor export all --format html(TUI 中为 e 键)导出的报告示例。它是单个 HTML 文件,用浏览器打开后选择“另存为 PDF”即可得到可提交给审计人员的 PDF。
RoamSwitch Sensor 审计报告
| 创建时间 | 2026年9月20日(日) 11:30:12 (UTC+9) |
|---|---|
| 站点 | 总部 3 楼服务器机房 |
| Sensor 公钥 | +kbYCoN5jJSykTAr8zDv/VCs2SdBcrwYbkCrzCRgsLM= |
| 审计日志 | 完整性验证:正常(未被篡改),18 条,head #18 771a265c58fa2f0a8990bc6be79ff5259d96a76a0a3fea472f308df02eaa087f |
各设备最新审计结果
| 设备 | 地址 | 执行时间 | 发现 | 开放端口 |
|---|---|---|---|---|
| web-prod-01 | 192.168.20.21 | 2026年9月20日(日) 11:00:43 (UTC+9) | 1 项 | 2 |
| db-prod-01 | 192.168.20.22 | 2026年9月20日(日) 11:01:14 (UTC+9) | 2 项 | 3 |
| dev-laptop-07 | 192.168.20.35 | 2026年9月20日(日) 11:02:07 (UTC+9) | 无问题 | 1 |
发现事项
| 时间 | 设备 | 端口 | 描述 | 建议措施 |
|---|---|---|---|---|
| 2026年9月20日(日) 11:01:14 (UTC+9) | db-prod-01 | 22 | SSH 版本横幅暴露 该 SSH 服务器在连接时会暴露版本横幅。横幅本身属于正常行为,但会成为攻击者缩小已知漏洞范围的线索。 | 请将 SSH 更新到最新版本,并根据需要精简横幅内容。 |
| 2026年9月20日(日) 11:01:14 (UTC+9) | db-prod-01 | 6379 | 已知漏洞:CVE-2021-32626 (Redis) NVD 说明(英文原文):Redis is an open source, in-memory database that persists on disk. In affected versions specially crafted Lua scripts executing in Redis can cause the heap-based Lua stack to be overflowed, due to incomplete checks for this condition. This can result with heap corruption and potentially remote code execution. This problem exists in all versions of Redis with Lua scripting support, starting from 2.6. The problem is fixed in versions 6.2.6, 6.0.16 and 5.0.14. | 请尽快将 Redis 升级到不受 CVE-2021-32626 影响的版本,在此之前请限制未经认证的网络访问。 |
| 2026年9月20日(日) 11:00:43 (UTC+9) | web-prod-01 | 22 | SSH 版本横幅暴露 该 SSH 服务器在连接时会暴露版本横幅。横幅本身属于正常行为,但会成为攻击者缩小已知漏洞范围的线索。 | 请将 SSH 更新到最新版本,并根据需要精简横幅内容。 |
| 2026年9月19日(土) 17:33:18 (UTC+9) | db-prod-01 | 22 | SSH 版本横幅暴露 该 SSH 服务器在连接时会暴露版本横幅。横幅本身属于正常行为,但会成为攻击者缩小已知漏洞范围的线索。 | 请将 SSH 更新到最新版本,并根据需要精简横幅内容。 |
设备台账(在局域网中观测到的所有设备)
| MAC | IP | 主机名 | 厂商 | RoamSwitch 管理 | 备注 |
|---|---|---|---|---|---|
| 00:1b:8b:3c:9a:07 | 192.168.20.1 | _gateway | NEC Platforms | 未管理 | 总部网关路由器 |
| 7c:8b:ca:61:d2:4e | 192.168.20.2 | TP-Link Technologies | 未管理 | 3 楼 Wi-Fi 接入点 | |
| e4:e7:49:2b:70:c1 | 192.168.20.3 | Hewlett Packard | 未管理 | 2 楼多功能一体机 | |
| 90:61:ae:17:4d:e2 | 192.168.20.21 | Intel Corporate | 已管理 | 生产 Web 服务器 | |
| 90:61:ae:17:4d:f9 | 192.168.20.22 | Intel Corporate | 已管理 | 生产数据库服务器 | |
| 04:20:9a:cc:31:8f | 192.168.20.31 | sensor-hq-01 | Panasonic AVC Networks Company | 未管理 | RoamSwitch-Sensor |
| a0:c9:a0:5e:83:2b | 192.168.20.35 | Murata Manufacturing | 已管理 | 开发用笔记本电脑 | |
| 8e:0f:95:a2:64:5d | 192.168.20.44 | 未管理 | |||
| 5e:e2:59:1d:c8:03 | 192.168.20.45 | 未管理 | |||
| a8:3b:76:9c:20:e4 | 192.168.20.52 | Cloud Network Technology Singapore PTE. | 未管理 |
操作与审批日志
| # | 时间 | 执行者 | 操作 | 适用对象 | 详情 |
|---|---|---|---|---|---|
| 18 | 2026年9月20日(日) 11:02:07 (UTC+9) | scheduler | audit_completed | dev-laptop-07 (Q9mW3sLp0xVc) | trigger=scheduled host=192.168.20.35 findings=0 open_ports=1 new_findings=0 resolved_findings=0 |
| 17 | 2026年9月20日(日) 11:02:05 (UTC+9) | scheduler | audit_started | dev-laptop-07 (Q9mW3sLp0xVc) | host=192.168.20.35 |
| 16 | 2026年9月20日(日) 11:01:14 (UTC+9) | scheduler | audit_completed | db-prod-01 (Zt4Kb8NwY1eR) | trigger=scheduled host=192.168.20.22 findings=2 open_ports=3 new_findings=1 resolved_findings=0 |
| 15 | 2026年9月20日(日) 11:01:12 (UTC+9) | scheduler | audit_started | db-prod-01 (Zt4Kb8NwY1eR) | host=192.168.20.22 |
| 14 | 2026年9月20日(日) 11:00:43 (UTC+9) | scheduler | audit_completed | web-prod-01 (Xk3F9aLm2QzB) | trigger=scheduled host=192.168.20.21 findings=1 open_ports=2 new_findings=1 resolved_findings=0 |
| 13 | 2026年9月20日(日) 11:00:41 (UTC+9) | scheduler | audit_started | web-prod-01 (Xk3F9aLm2QzB) | host=192.168.20.21 |
| 12 | 2026年9月19日(土) 18:11:40 (UTC+9) | cli:uid=1000 | config_changed | schedule.window_end_hour | value=5 |
| 11 | 2026年9月19日(土) 18:11:32 (UTC+9) | cli:uid=1000 | config_changed | schedule.window_start_hour | value=1 |
| 10 | 2026年9月19日(土) 18:10:02 (UTC+9) | cli:uid=1000 | config_changed | schedule.enabled | value=true |
| 9 | 2026年9月19日(土) 17:47:19 (UTC+9) | control_api: | pair | dev-laptop-07 (Q9mW3sLp0xVc) | endpoint redeemed an operator-issued pairing code and was added to the audit scope |
| 8 | 2026年9月19日(土) 17:46:52 (UTC+9) | cli:uid=1000 | pairing_code_issued | single-use, valid 10 minutes | |
| 7 | 2026年9月19日(土) 17:33:18 (UTC+9) | cli:uid=1000 | audit_completed | db-prod-01 (Zt4Kb8NwY1eR) | trigger=manual host=192.168.20.22 findings=1 open_ports=2 new_findings=1 resolved_findings=0 |
| 6 | 2026年9月19日(土) 17:33:15 (UTC+9) | cli:uid=1000 | audit_started | db-prod-01 (Zt4Kb8NwY1eR) | manual audit; host=192.168.20.22 |
| 5 | 2026年9月19日(土) 17:31:07 (UTC+9) | control_api: | pair | db-prod-01 (Zt4Kb8NwY1eR) | endpoint redeemed an operator-issued pairing code and was added to the audit scope |
| 4 | 2026年9月19日(土) 17:30:41 (UTC+9) | cli:uid=1000 | pairing_code_issued | single-use, valid 10 minutes | |
| 3 | 2026年9月19日(土) 17:12:26 (UTC+9) | control_api: | pair | web-prod-01 (Xk3F9aLm2QzB) | endpoint redeemed an operator-issued pairing code and was added to the audit scope |
| 2 | 2026年9月19日(土) 17:11:58 (UTC+9) | cli:uid=1000 | pairing_code_issued | single-use, valid 10 minutes | |
| 1 | 2026年9月19日(土) 17:00:03 (UTC+9) | daemon | daemon_started | version 0.3.4 |
RoamSwitch Sensor Audit Report
| Generated | Sun, 2026-09-20 02:30:12 (UTC) |
|---|---|
| Site | HQ – 3F server room |
| Sensor public key | +kbYCoN5jJSykTAr8zDv/VCs2SdBcrwYbkCrzCRgsLM= |
| Audit log | Integrity check: OK (no tampering detected) — 18 entries, head #18 771a265c58fa2f0a8990bc6be79ff5259d96a76a0a3fea472f308df02eaa087f |
Latest audit per endpoint
| Endpoint | Address | Timestamp | Findings | Open ports |
|---|---|---|---|---|
| web-prod-01 | 192.168.20.21 | Sun, 2026-09-20 02:00:43 (UTC) | 1 finding(s) | 2 |
| db-prod-01 | 192.168.20.22 | Sun, 2026-09-20 02:01:14 (UTC) | 2 finding(s) | 3 |
| dev-laptop-07 | 192.168.20.35 | Sun, 2026-09-20 02:02:07 (UTC) | clean | 1 |
Findings
| When | Endpoint | Port | Finding | Recommendation |
|---|---|---|---|---|
| Sun, 2026-09-20 02:01:14 (UTC) | db-prod-01 | 22 | SSH Version Banner Disclosed This SSH server discloses its version banner on connect. This is normal SSH behavior, but the banner gives an attacker a starting point to look up known vulnerabilities for that version. | Keep SSH updated to the latest version, and minimize the banner's detail if your SSH implementation allows it. |
| Sun, 2026-09-20 02:01:14 (UTC) | db-prod-01 | 6379 | Known Vulnerability: CVE-2021-32626 (Redis) Redis is an open source, in-memory database that persists on disk. In affected versions specially crafted Lua scripts executing in Redis can cause the heap-based Lua stack to be overflowed, due to incomplete checks for this condition. This can result with heap corruption and potentially remote code execution. This problem exists in all versions of Redis with Lua scripting support, starting from 2.6. The problem is fixed in versions 6.2.6, 6.0.16 and 5.0.14. | Upgrade Redis to a version not affected by CVE-2021-32626 as soon as possible, and restrict unauthenticated network access to it in the meantime. |
| Sun, 2026-09-20 02:00:43 (UTC) | web-prod-01 | 22 | SSH Version Banner Disclosed This SSH server discloses its version banner on connect. This is normal SSH behavior, but the banner gives an attacker a starting point to look up known vulnerabilities for that version. | Keep SSH updated to the latest version, and minimize the banner's detail if your SSH implementation allows it. |
| Sat, 2026-09-19 08:33:18 (UTC) | db-prod-01 | 22 | SSH Version Banner Disclosed This SSH server discloses its version banner on connect. This is normal SSH behavior, but the banner gives an attacker a starting point to look up known vulnerabilities for that version. | Keep SSH updated to the latest version, and minimize the banner's detail if your SSH implementation allows it. |
Device inventory (every device observed on the LAN)
| MAC | IP | Hostname | Vendor | Managed | Note |
|---|---|---|---|---|---|
| 00:1b:8b:3c:9a:07 | 192.168.20.1 | _gateway | NEC Platforms | no | HQ gateway router |
| 7c:8b:ca:61:d2:4e | 192.168.20.2 | TP-Link Technologies | no | 3F Wi-Fi access point | |
| e4:e7:49:2b:70:c1 | 192.168.20.3 | Hewlett Packard | no | 2F multifunction printer | |
| 90:61:ae:17:4d:e2 | 192.168.20.21 | Intel Corporate | yes | Production web server | |
| 90:61:ae:17:4d:f9 | 192.168.20.22 | Intel Corporate | yes | Production database server | |
| 04:20:9a:cc:31:8f | 192.168.20.31 | sensor-hq-01 | Panasonic AVC Networks Company | no | RoamSwitch-Sensor |
| a0:c9:a0:5e:83:2b | 192.168.20.35 | Murata Manufacturing | yes | Development laptop | |
| 8e:0f:95:a2:64:5d | 192.168.20.44 | no | |||
| 5e:e2:59:1d:c8:03 | 192.168.20.45 | no | |||
| a8:3b:76:9c:20:e4 | 192.168.20.52 | Cloud Network Technology Singapore PTE. | no |
Operation & approval log
| # | When | Actor | Action | Target | Detail |
|---|---|---|---|---|---|
| 18 | Sun, 2026-09-20 02:02:07 (UTC) | scheduler | audit_completed | dev-laptop-07 (Q9mW3sLp0xVc) | trigger=scheduled host=192.168.20.35 findings=0 open_ports=1 new_findings=0 resolved_findings=0 |
| 17 | Sun, 2026-09-20 02:02:05 (UTC) | scheduler | audit_started | dev-laptop-07 (Q9mW3sLp0xVc) | host=192.168.20.35 |
| 16 | Sun, 2026-09-20 02:01:14 (UTC) | scheduler | audit_completed | db-prod-01 (Zt4Kb8NwY1eR) | trigger=scheduled host=192.168.20.22 findings=2 open_ports=3 new_findings=1 resolved_findings=0 |
| 15 | Sun, 2026-09-20 02:01:12 (UTC) | scheduler | audit_started | db-prod-01 (Zt4Kb8NwY1eR) | host=192.168.20.22 |
| 14 | Sun, 2026-09-20 02:00:43 (UTC) | scheduler | audit_completed | web-prod-01 (Xk3F9aLm2QzB) | trigger=scheduled host=192.168.20.21 findings=1 open_ports=2 new_findings=1 resolved_findings=0 |
| 13 | Sun, 2026-09-20 02:00:41 (UTC) | scheduler | audit_started | web-prod-01 (Xk3F9aLm2QzB) | host=192.168.20.21 |
| 12 | Sat, 2026-09-19 09:11:40 (UTC) | cli:uid=1000 | config_changed | schedule.window_end_hour | value=5 |
| 11 | Sat, 2026-09-19 09:11:32 (UTC) | cli:uid=1000 | config_changed | schedule.window_start_hour | value=1 |
| 10 | Sat, 2026-09-19 09:10:02 (UTC) | cli:uid=1000 | config_changed | schedule.enabled | value=true |
| 9 | Sat, 2026-09-19 08:47:19 (UTC) | control_api: | pair | dev-laptop-07 (Q9mW3sLp0xVc) | endpoint redeemed an operator-issued pairing code and was added to the audit scope |
| 8 | Sat, 2026-09-19 08:46:52 (UTC) | cli:uid=1000 | pairing_code_issued | single-use, valid 10 minutes | |
| 7 | Sat, 2026-09-19 08:33:18 (UTC) | cli:uid=1000 | audit_completed | db-prod-01 (Zt4Kb8NwY1eR) | trigger=manual host=192.168.20.22 findings=1 open_ports=2 new_findings=1 resolved_findings=0 |
| 6 | Sat, 2026-09-19 08:33:15 (UTC) | cli:uid=1000 | audit_started | db-prod-01 (Zt4Kb8NwY1eR) | manual audit; host=192.168.20.22 |
| 5 | Sat, 2026-09-19 08:31:07 (UTC) | control_api: | pair | db-prod-01 (Zt4Kb8NwY1eR) | endpoint redeemed an operator-issued pairing code and was added to the audit scope |
| 4 | Sat, 2026-09-19 08:30:41 (UTC) | cli:uid=1000 | pairing_code_issued | single-use, valid 10 minutes | |
| 3 | Sat, 2026-09-19 08:12:26 (UTC) | control_api: | pair | web-prod-01 (Xk3F9aLm2QzB) | endpoint redeemed an operator-issued pairing code and was added to the audit scope |
| 2 | Sat, 2026-09-19 08:11:58 (UTC) | cli:uid=1000 | pairing_code_issued | single-use, valid 10 minutes | |
| 1 | Sat, 2026-09-19 08:00:03 (UTC) | daemon | daemon_started | version 0.3.4 |
所展示的机器名、MAC 地址、IP 地址和公钥均为虚构。报告正文可用显示语言(10 种语言)输出,此处展示的是日语版和英语版示例(非日语显示时展示英语版)。